
Sentramesh and Emerging AI Governance Standards

Executive Summary
As organisations rapidly deploy autonomous and agentic AI systems, governance is becoming a board-level priority. Three significant standards released in 2026 establish new expectations for AI cybersecurity, quality management, and organisational governance: ISO/IEC 27090:2026 (AI Cybersecurity), EN 18286:2026 (EU AI Act Quality Management Systems), and IEEE 2863-2026 (Organisational AI Governance).
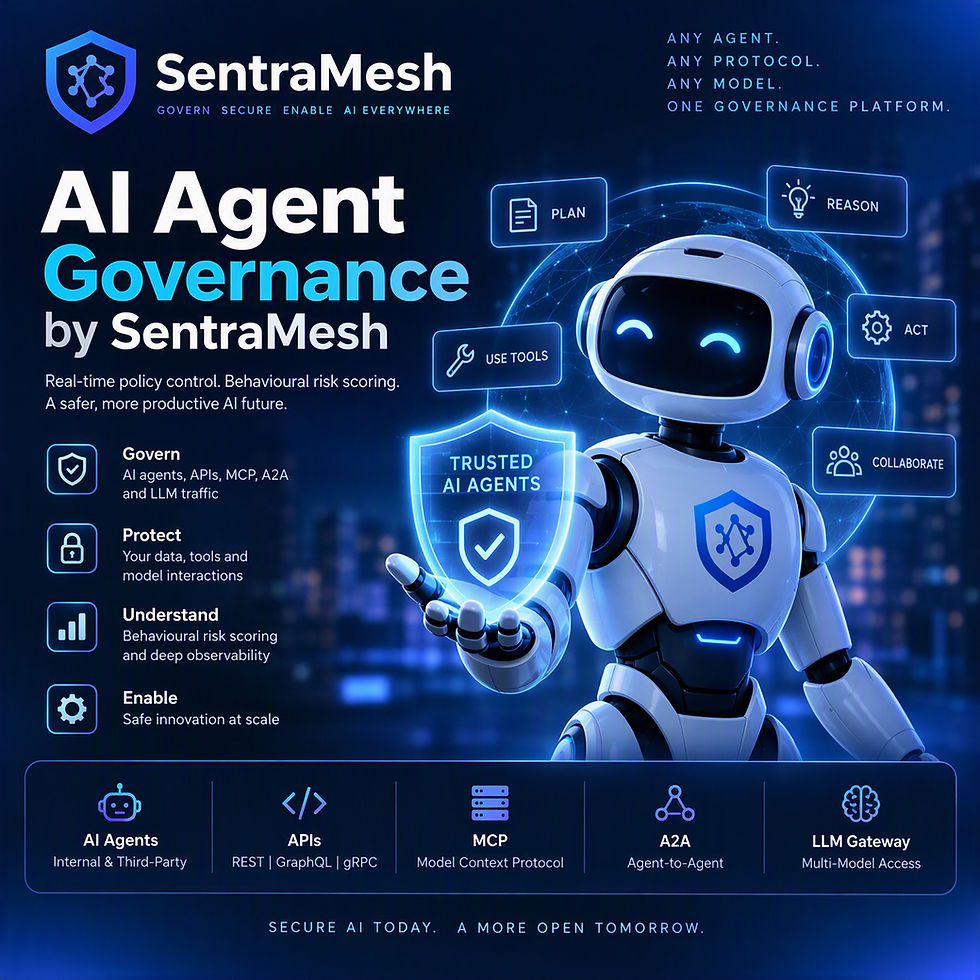
Sentramesh is positioned as an AI Governance Control Plane that provides real-time visibility, policy enforcement, behavioural risk monitoring, and audit-ready evidence for autonomous AI systems. While Sentramesh is not a complete compliance framework on its own, it can serve as a foundational governance layer that helps enterprises operationalise compliance requirements and demonstrate ongoing control of AI systems.
Strategic Value of Sentramesh
Sentramesh addresses one of the largest governance challenges facing enterprises today: maintaining control over AI systems that can act autonomously, access data, invoke applications, and make operational decisions.
Centralised governance of AI agents
Real-time monitoring and visibility
Behavioural risk scoring
Continuous policy enforcement
Compliance reporting
Immutable audit trails
Automated governance controls
These capabilities create the operational evidence and oversight mechanisms increasingly expected by regulators, auditors, and governing boards.
Alignment with ISO/IEC 27090:2026
ISO/IEC 27090 provides guidance for identifying, detecting and mitigating AI-specific cybersecurity threats throughout the AI lifecycle, including data poisoning, model theft, model extraction, compromised training or retraining data, and AI-specific attack vectors and vulnerabilities.
SentraMesh supports these objectives by monitoring AI agent behaviour in real time, detecting anomalous or unauthorised activities, enforcing security policies dynamically, providing governance controls across AI operations, and creating traceable evidence for security investigations and audits.
Executive assessment: Alignment is strong.
Alignment with EN 18286:2026
EN 18286 establishes a quality management framework supporting Article 17 of the EU AI Act, particularly for high-risk AI systems. It focuses on governance processes, lifecycle management, risk management, documentation, change control, post-market monitoring, and regulatory evidence generation.
Sentramesh provides continuous monitoring of deployed AI systems, policy lifecycle management, governance workflow enforcement, audit-ready reporting, traceability of AI actions and decisions, and compliance evidence generation.
Executive assessment: Alignment is strong but complementary. EN 18286 requires a broader enterprise quality management system encompassing organisational processes, documentation, supplier oversight, and management accountability. Sentramesh can provide the operational governance and evidence layer needed to support these requirements, but it is not a replacement for the full QMS.
Alignment with IEEE 2863-2026
IEEE 2863 provides guidance for responsible organisational governance of AI, focusing on accountability, transparency, ethical oversight, governance processes, auditing, training, compliance assurance, and responsible AI operations.
Sentramesh aligns particularly well by enabling full visibility into AI behaviour, transparent governance controls, accountability through audit trails, continuous compliance monitoring, centralised policy management, and operational oversight of autonomous agents.
Executive assessment: Alignment is very strong. Among the three standards, IEEE 2863 is the most directly aligned with Sentramesh's mission of providing governance and oversight for autonomous AI systems.
Governance Coverage Summary
Across ISO/IEC 27090, EN 18286, and IEEE 2863, Sentramesh supports real-time AI monitoring, policy enforcement, behavioural risk detection, audit trails, compliance evidence, and lifecycle oversight. Organisational accountability, quality management support, and board-level governance support vary by standard and should be complemented by enterprise governance processes.
Conclusion
Sentramesh should be viewed as a strategic AI Governance Control Plane that provides the operational controls, visibility, and evidence required by next-generation AI governance standards.
Reduce AI-related cybersecurity risks
Demonstrate AI Act readiness
Establish governance over autonomous agents
Improve auditability and regulatory confidence
Accelerate alignment with emerging international AI standards
While organisations will still require governance committees, policies, risk frameworks, and quality management processes, Sentramesh provides the technology foundation that turns governance principles into measurable and enforceable operational controls. This positions the platform as a key enabler of compliance with ISO/IEC 27090, EN 18286, and IEEE 2863, while helping organisations scale AI adoption with confidence.

Comments